Cybersecurity and Cyber GRC consultingFort Worth, Texas. Founded 2016.

Cybersecurity that protects the business. Not just the audit.

  • Customers need proof.
  • Requirements keep changing.
  • Risks need attention.
  • Your team is stretched thin.

And somehow, all of it lands on you.

Hotman Group is a CPA-led cybersecurity and Cyber GRC consulting firm. We bring business judgment, security expertise, and the people to do the work: assessment, remediation, implementation, and ongoing operations.

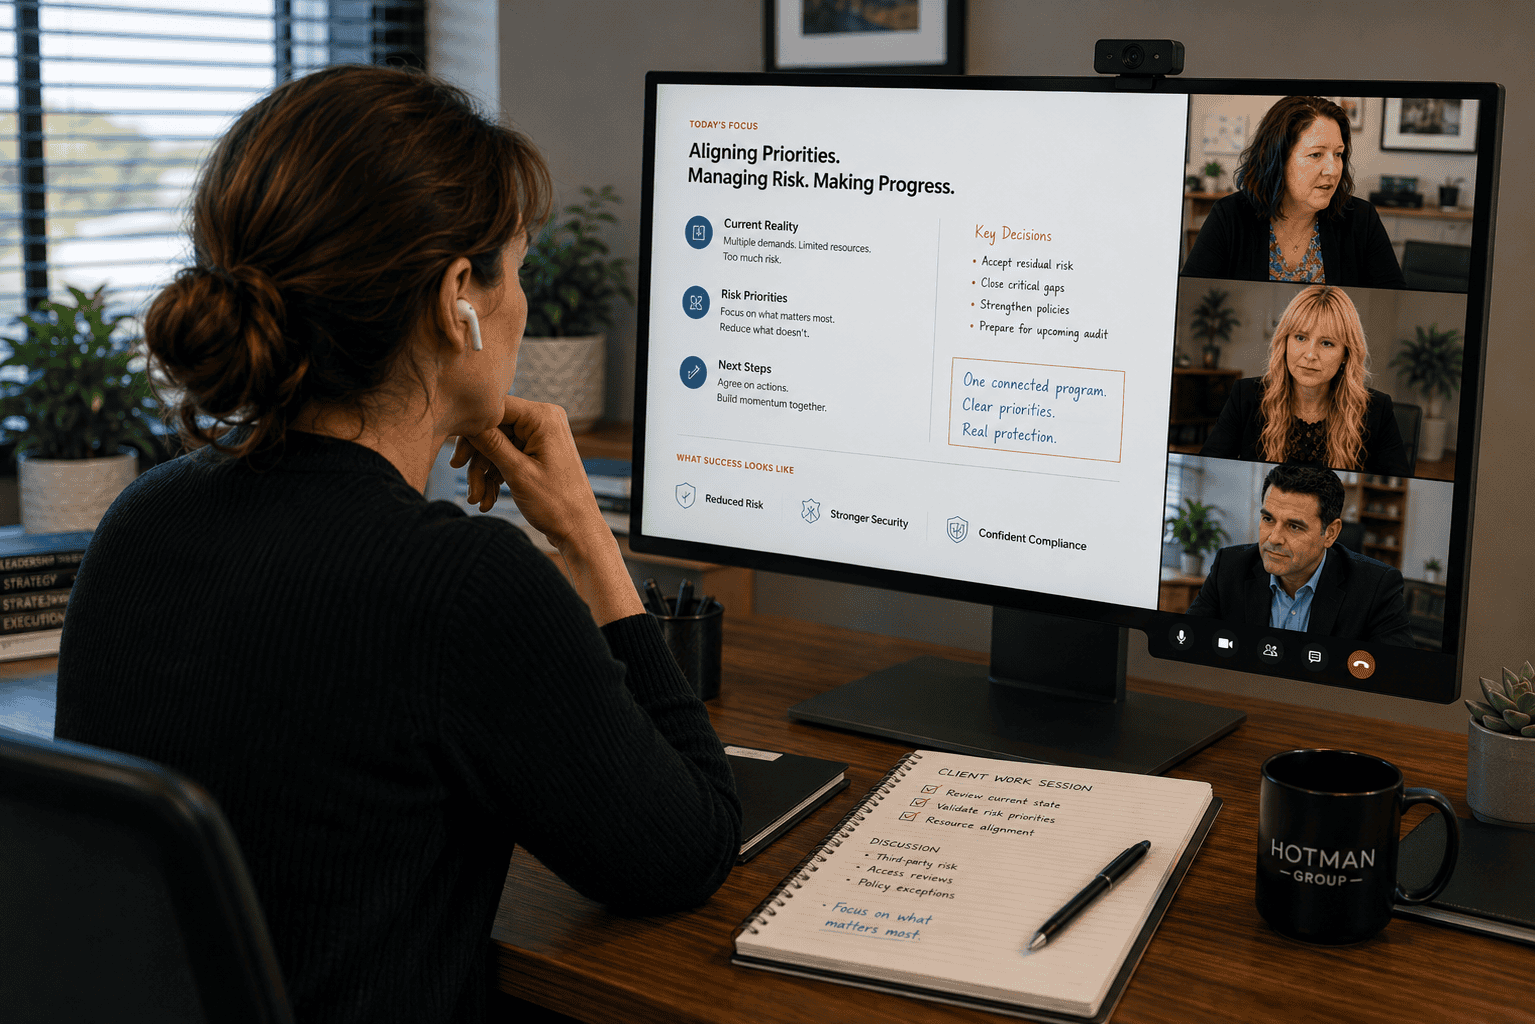
A cybersecurity leader on a video call reviewing priorities, risk decisions, and next steps.
How HG worksSenior judgment, hands-on delivery, and a team that stays involved.
Business, finance, and security judgmentCPA-led
We assess, fix, implement, and operateHands-on delivery
Four verified client reviews
Certified woman-owned small businessWOSB

Selected client outcomes

Complex problems. Work that changes the outcome.

Three situations clients brought us, and what changed for the business.

Customer security review Won

A major banking contract, without taking on unnecessary requirements.

Situation
Pre-contract security review beyond normal industry practice
HG's role
Turned each request into a risk decision, with alternative controls where appropriate
Result
A defensible security position, and the contract
Read the banking contract case
GRC technology 95%

Audit evidence reused. More audit volume, no added headcount.

Client
Trintech
Tools
20+ consolidated into one GRC platform
Audit volume
Up 33%, without additional resources
“Hotman Group and StandardFusion helped us move from manual processes to a system that drives itself.”Jerry Koshy, Director of Compliance and Audit, Trintech
Read the Trintech case
Ongoing vGRC 400+

Controls operated across five frameworks, without growing the internal team.

Frameworks
Five, plus HIPAA and NIST CSF assessments
Duration
Nearly five years as an extension of the team
HG's role
Control monitoring, remediation priorities, audit organization
Read the ongoing vGRC case

Our work spans federal and defense contractors, public SaaS and AI companies, organizations serving the financial sector, and health and wellness organizations, from first programs to complex multi-framework environments.

See all client results

The cost of waiting

When the work doesn't get done, the business feels it.

The work isn't hard to find. It's hard to finish with a team that already has a day job.

  • Deals stall.A customer security review can hold up a contract until you can show the right protection.
  • Findings return.Fixing for the auditor instead of the cause brings the same issues back next year.
  • Risk goes unowned.Without clear owners, leadership can't tell what is actually being managed.
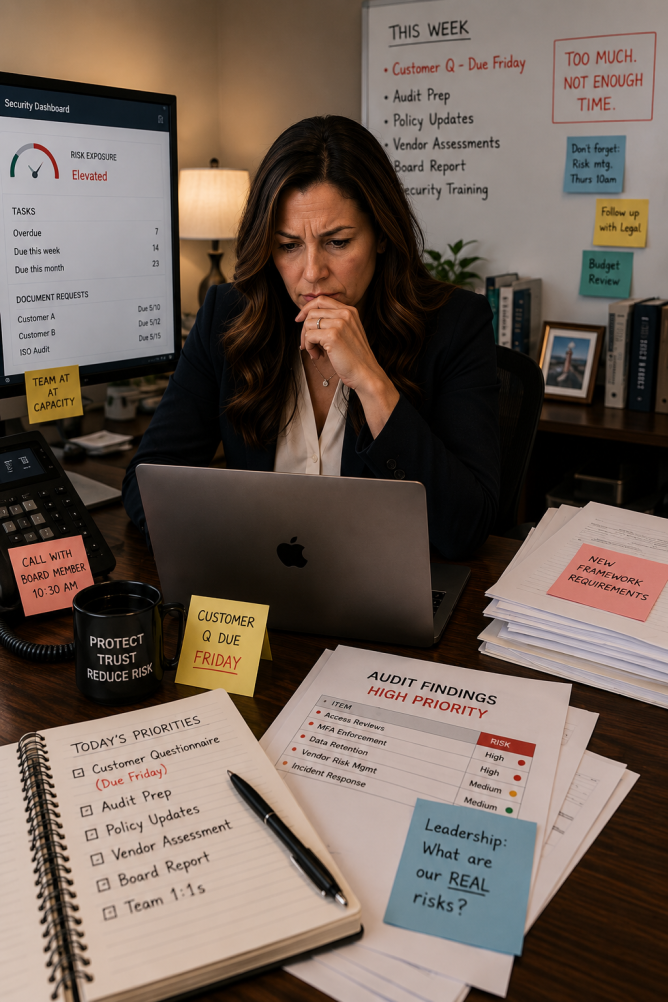
Cybersecurity leader balancing customer requirements, audit findings, risk questions, and limited team capacity.

Meanwhile, on your desk

  • CustomerAnother security questionnaire.
  • New frameworkA requirement nobody planned for this year.
  • AuditA finding that needs to be fixed, not just answered.
  • Leadership"Where is our real risk?"
  • GRC platformBought to make this easier. Somehow it created more work.

The hard part isn't finding information. It's getting the work done with limited people, time, and expertise.

That's where we come in.

We help you figure out what's actually broken and what matters most. Then we help you get it done.

Talk With Us

Why Hotman Group

We don't hand you a report and wish you luck.

We bring business, financial, cybersecurity, technology, and GRC judgment to the same problem, and the people to act on it.

How we think: one real decision
What the client was ready to buyA CMMC gap assessment

Tens of thousands of dollars, before anyone knew where CUI lived.

The question we asked firstWhere does CUI actually live?

Seven ERP systems, and a major technology transformation underway.

What we recommendedScope first. Then assess.

So the assessment would evaluate the right environment.

See the case

We challenge the wrong answer.

Sometimes the right advice is not to buy the tool or run the assessment yet.

We build for after the audit.

Owners know what to do. Leadership sees what remains at risk.

0 nonconformities, and still 51 improvements found

Cheri Hotman founded HG in May 2016. CPA, MBA, CISSP, CCISO, CMMC CCP. Author of Rebuilding Cybersecurity (forthcoming, CRC Press). Trent Hotman, Managing Partner. Fort Worth, Texas. Certified WOSB.

Meet the HG team

How we help

Four situations we're brought in to solve.

Security and GRC decisions are piling up, and no one senior has the time to own them.

Fractional CISO (vCISO) and vGRC support

Senior ownership of priorities, risk, and controls, without another full-time executive.

A customer, contract, or regulator asks for SOC 2, ISO 27001, CMMC, or a requirement you didn't see coming.

Security and compliance readiness

Scope what applies, close the gaps, and meet the requirement without a new silo.

You're choosing a GRC platform, or the one you bought isn't delivering what you expected.

GRC platform selection and implementation

Independent selection, implementation, or rescue, built around your controls and owners.

Findings keep coming back, security processes aren't working, or you need to know where you really stand.

Cybersecurity assessments and remediation

Root causes found, real risk prioritized, and fixes verified in practice.

Many requirements, one foundation

The frameworks change. The security work has to connect.

A new obligation shouldn't mean starting over. We connect overlapping requirements to the controls, evidence, owners, and decisions that make protection work.

See how we approach new requirements
  • NIST CSF
  • ISO 27001
  • SOC 2
  • HIPAA
  • CMMC
  • PCI DSS
  • FedRAMP
  • CIS Controls
  • And others
One operating programShared controls, reusable evidence, clear owners, and decisions that hold up.

How it begins

A clear way forward in three steps.

You don't need to know exactly what's needed before you call.

Talk With Us
  1. Tell us what's going on.

    One conversation about the problem, the pressure behind it, and what you're being asked to deliver.

  2. Agree on what needs to happen.

    A scope that fits the real problem: a focused Health Check, a defined project, or ongoing support.

  3. Get it done.

    We do the work alongside your team and stay involved as long as it's useful.

What changes

Less activity for the sake of compliance. More control over risk.

  • Separate audits and evidence requestsEvidence reused across frameworks
  • Findings without practical ownershipOwned, tracked fixes
  • Tools that create more administrationA platform that runs the work
  • Policies that don't reflect how work happensControls checked between audits
  • ⅔ fewer mapped controls across SOX ITGC, SOC 1, and SOC 2 at a public SaaS company. Read the case
  • 3+ risk registers unified into one view leadership could act on. Read the case

Know where your risks stand, and be able to prove it.

See what your team is doing about the risks that matter, and what you can show customers, leadership, and auditors.

Bring us the problem. We'll help figure out what needs to happen.

Talk With Us Certified Woman-Owned Small Business (WOSB)